Six directions. One office that answers for all of them
ISMO is an outsourced internal security office on a standing subscription. We check people and we set up the processes they work in — from the first interview to the last day, from access rights to evidence.
Directions turn one at a time. Click one to hold it.
- Background verified — including why the last job really ended
- Hidden ties, second jobs and conflicts of interest
- Re-checks while they work, not only before the offer
- Offboarding: access revoked, assets back, exit on record
- Any internal chain walked end to end — approvals, purchasing, hiring, data
- Steps where one person can start, approve and benefit alone
- Control points that live in the system, not only on paper
- Written procedures that match what people actually do
- Rights compared against what each role actually needs
- Shared logins, dormant accounts, duties that should be split
- Credentials that outlived the contract
- A reviewed access map, not an export from the admin panel
- Protocols for laptops and phones — company and personal
- Messenger rules for Telegram, WhatsApp and Signal
- The first fifteen minutes after a device is lost or seized
- Travel and border mode for people who carry the company
- Sweeps of offices, homes and vehicles for planted devices
- Detection of interception equipment and hidden transmitters
- Who can physically enter which room — and who would notice
- What the company and its key people expose in public
- The incident recorded: nature, scale, consequences
- Evidence preserved so it still counts later
- Interviews inside a lawful internal procedure
- Criminal, civil and commercial follow-through across jurisdictions
The person who costs you most is already on payroll
Your finance lead, your key account manager, the contractor who still has production access six months after leaving. Everything they do is authorised, so nothing is ever flagged. Internal loss is not a breach — it is a decision made by someone you hired.
So we start earlier. Every candidate is checked before the offer goes out — identity, history, exposure, affiliations — and checked again while they work. The cheapest incident is the one that never joins the company.
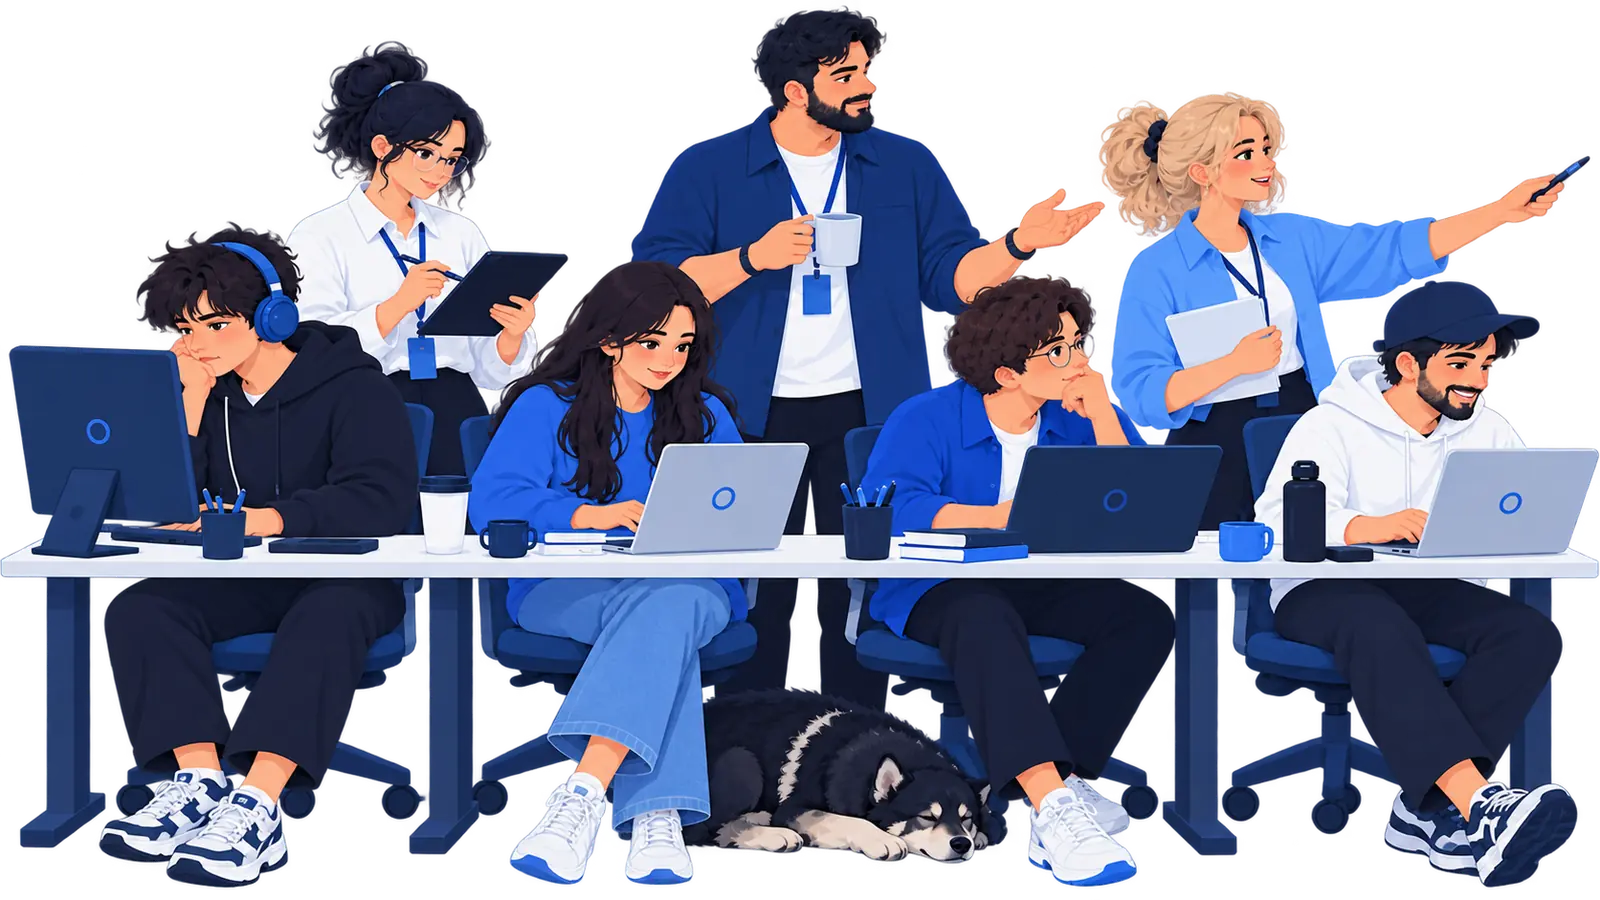
Every person in the illustration is a button: hover or focus shows who it is, activating it runs a screening check and opens the form.
Backend engineer
Not recommended- Identity
- Confirmed
- Employment history
- Confirmed — but still has live access at two former clients
- Financial vulnerability
- None found
- Connections & conflicts
- None found
- Public footprint
- Company code in a personal repository
- Devices
- Laptop outside company management
Keys that outlived the contract. Revoke before anything else.
HR lead
Recommended- Identity
- Confirmed
- Employment history
- 5 years, confirmed
- Financial vulnerability
- None found
- Connections & conflicts
- None found
- Public footprint
- Clean
- Devices
- Managed
No conflicts. Routine re-check in a quarter.
Key account manager
Not recommended- Identity
- Confirmed
- Employment history
- Confirmed
- Financial vulnerability
- None found
- Connections & conflicts
- Client chats kept in a personal messenger
- Public footprint
- Clean
- Devices
- Client base synced to a personal cloud
Your most valuable data on a phone you do not control.
Country manager
Not recommended- Identity
- Confirmed
- Employment history
- Confirmed
- Financial vulnerability
- Undeclared consulting income
- Connections & conflicts
- Advises a competitor
- Public footprint
- Meetings not disclosed
- Devices
- Large exports out of hours
Strategy is leaving the building. Isolate access, then investigate.
Payments analyst
Not recommended- Identity
- Confirmed
- Employment history
- Approved his own requests 11 times
- Financial vulnerability
- Payments to a supplier he controls
- Connections & conflicts
- Undeclared company of his own
- Public footprint
- Clean
- Devices
- Managed
A pattern, not an accident. Remove approval rights today.
Head of compliance
Recommended- Identity
- Confirmed
- Employment history
- 8 years, confirmed
- Financial vulnerability
- None found
- Connections & conflicts
- None found
- Public footprint
- Clean
- Devices
- Managed
Clean. Full access justified.
Support team lead
Recommended- Identity
- Confirmed
- Employment history
- 2 years, confirmed
- Financial vulnerability
- None found
- Connections & conflicts
- None found
- Public footprint
- Clean
- Devices
- Managed
Clean. Standard monitoring.
Office dog · Rufus
Recommended- Identity
- Microchipped, confirmed
- Employment history
- 3 years, no gaps
- Financial vulnerability
- Paid in treats
- Connections & conflicts
- Only under the desk
- Public footprint
- Not on social media
- Devices
- Chews none
Slept through every incident. Has never leaked a single byte.
We do not only check people. We set up the processes they work in
Any internal process — approvals, purchasing, hiring, access, data, offboarding — is a chain of steps. Internal loss almost never needs a clever scheme. It needs one step where control is missing. We walk the chain, find the weak joint and write the rule that closes it.
Any process, five questions. Select a step.
What we look at
Who is allowed to begin this process at all, and whether that right belongs to a named person or to a login several people share.
What usually breaks
A step anyone with the password can start, with no trace of who actually did.
What we look at
Where the decision is really made, who can override it, and whether an exception is recorded anywhere.
What usually breaks
A control that lives in the regulation and not in the system — and everybody knows the way around it.
What we look at
Whether the person who decides is separated from the person who performs, and what happens on the days they are the same.
What usually breaks
One role holding the whole chain end to end, because it was convenient once and nobody revisited it.
What we look at
Who can read, copy or change what the process produced, and for how long after they stopped needing it.
What usually breaks
Rights opened for a single task and never narrowed again.
What we look at
Who confirms it happened as intended, against which source, and who can edit the record afterwards.
What usually breaks
The person who performed the step is also the one who signs off that it was correct.
The output is not a list of findings. It is a written procedure, the control points that were missing, and the access map that belongs with it.
Who has access to your money — and who they are friends with
An access list shows who can do something. It never shows who will do it together. In a business that runs on traffic, most losses are not a break-in: they are a few people with legitimate access who came to an agreement. Below, a composite story.
A composite of typical cases.
-
Month 0
One of us
The founder hires a media-buying team lead on an old friend's word: “He runs green, has his own setups, no need to check him.” On day one he gets every ad account, the tracker and the network logins. A month later they celebrate a record month together. “He's like a brother,” the founder says.
Signal nobody acted on: Full access on day one, no background check
-
Month 3
The group chat
He gets close to the finance manager who tops up the accounts and pays the agencies. In passing he learns which payment providers handle payouts, what the limits are and who approves USDT transfers.
Signal nobody acted on: A buyer asking about payouts and wallets
-
Month 7
A reliable agency
He brings in an account agency: fresh ad accounts, their own farm, “the best terms on the market”. The owner went to university with him. Finance pays the invoices without reconciling them, straight to a wallet.
Signal nobody acted on: A new contractor with no history, paid to a personal wallet
-
Year 1
Just under the limit
The agency's fee runs 8–12 % above market, and the difference is split three ways. Part of his best traffic goes elsewhere under his sub IDs: the report says conversion dipped, and someone else is in profit.
Signal nobody acted on: ROI drops only on his streams; the tracker and the network disagree
-
Year 1.5
Setups walk out
His best setups and creatives turn up at a competitor a week after launch. He tells the team: “Someone spied them, that's the market.” Everyone nods, because it does happen.
Signal nobody acted on: Tracker exports in the middle of the night
-
Year 2
Difficult
An analyst reconciles the tracker with the network's numbers and shows the founder the gap. “She doesn't get how buying works,” says the team lead. She is moved off the buying team and leaves six months later.
Signal nobody acted on: Her warning was never written down
-
Year 3
He leaves with the team
He moves to a competitor with three buyers, the setups and every network manager's contact. For another month the ad accounts are still his, the agency keeps invoicing and the finance manager stays. The founder hears it from a network manager: “Your ex is already running on the same accounts.”
Signal nobody acted on: Access still live, contractor still paid
What actually happens with access
- Payouts and top-ups go to employees' personal wallets
- Ad-account and tracker access stays after someone leaves
- A new contractor with no history gets straight to the budget
- Nobody reconciles sub IDs and streams against the network's numbers
- The same person requests account top-ups and approves the agency's invoice
- Setups and creatives are exported with no trace of who or when
- The same contractor is approved every month just under the limit
- One person holds every network-manager contact
4 more
- The same person requests account top-ups and approves the agency's invoice
- Setups and creatives are exported with no trace of who or when
- The same contractor is approved every month just under the limit
- One person holds every network-manager contact
Nobody hacked anything — he was simply trusted with everything. A Risk X-Ray shows who holds which access and who is connected to whom.
Request a Risk X-Rayis how long the typical internal fraud runs before anyone finds it.
ACFE, Occupational Fraud 2026of cases come to light through a tip from a person, not through a control.
ACFE, Occupational Fraud 2026on average to contain an insider incident once it is found (global average per organisation).
Ponemon / DTEX, Cost of Insider Risks 2026Most of your business now happens on a phone you may not own
Deals are agreed in Telegram, files travel through WhatsApp, and the laptop that holds the client base is the same one the family uses at the weekend. These are the ways in that people who watch companies actually use. Close them one by one.
A list of nine real vulnerabilities. Activating one marks its countermeasure as set, shows a short explanation and installs it on the laptop and phone shown beside the list. When all nine are set, the devices show they are protected. Activating a set item again while it is open removes the mark.
-
How it happens. Commercial spyware such as Pegasus has infected fully updated iPhones through a single iMessage, with no tap from the victim. It is bought to watch executives, lawyers and journalists.
What we set up. A hardened profile for high-risk people, updates within 48 hours, daily restarts, a separate phone for travel.
Hardened profile: onUpdate window: 48 hDaily restart: scheduled# 01 · zero-click spywarepolicy phone.hardening {profile = "high-risk"updates = within(48h)restart = daily("04:00")travel = separate_device}apply → phone ✓ -
How it happens. Telegram accounts are stolen by talking people into sharing a login code. WhatsApp “GhostPairing” quietly links the attacker's device, and every chat is mirrored.
What we set up. A cloud password and PIN on every messenger, regular review of linked devices and sessions, and one rule: codes are never shared.
Two-step password: setLinked devices: 2 removedActive sessions: reviewed# 02 · messenger takeoverpolicy messengers {cloud_password = requiredpin = requiredsessions = review("7d")login_codes = never_share}unlink → 2 devicesapply → phone, laptop ✓ -
How it happens. Someone at the carrier is persuaded or paid to move your number to a new SIM. Every SMS code — and every password reset — then goes to someone else.
What we set up. A port-out PIN with the carrier, no SMS as a second factor, account recovery that does not rely on a personal e-mail.
Carrier PIN: setSMS codes → authenticatorRecovery e-mail: corporate# 03 · SIM swappolicy carrier {port_out_pin = setsms_codes = disabledsecond_factor = authenticatorrecovery_mail = corporate}apply → phone ✓ -
How it happens. A colleague, a driver or a partner who has seen your passcode needs two minutes alone with the device to install stalkerware or copy the chats.
What we set up. A strong passcode nobody watches you type, a short auto-lock, alerts on new sessions and a check for monitoring apps.
Auto-lock: 30 sNew-session alerts: onMonitoring apps: none found# 04 · two minutes unlockedpolicy device.lock {auto_lock = 30snew_sessions = alert}scan monitoring_apps → 0 foundapply → phone, laptop ✓ -
How it happens. Cables with hidden implants exist that record keystrokes and take control of the device. Gifts and borrowed chargers are the usual way in.
What we set up. Own cables only, data-blocking adapters for travel, gifted electronics checked before use.
USB data while charging: blockedCables and chargers: inventoried# 05 · untrusted cablespolicy usb {data_on_charge = blocktravel_adapter = data_blockergifted_devices = inspect_first}apply → phone, laptop ✓ -
How it happens. A chat deleted on the phone often lives on in a cloud backup — behind an old password, or shared with a family account.
What we set up. A backup policy, end-to-end encrypted backups, old devices wiped and removed from the account.
Backups: end-to-end encryptedOld devices: 3 removed# 06 · backupspolicy backup {encryption = end_to_endold_devices = wipe + unlink}unlink → 3 devicesapply → phone ✓ -
How it happens. At a border or during a search you can be required to unlock the device. Everything on it can then be copied in minutes.
What we set up. Travel mode: a minimal device, signed-out accounts, and a fifteen-minute protocol for loss or seizure.
Travel profile: readySeizure protocol: loaded# 07 · border & searchprofile travel {device = minimalaccounts = signed_outon_seize = protocol("15m")}apply → phone, laptop ✓ -
How it happens. Third-party keyboards, “cleaner” and free VPN apps, browser extensions: they can read what you type and open your files. A permission granted once stays forever.
What we set up. An approved app list, a review of microphone, camera and file permissions, no third-party keyboards on work devices.
Permissions: 14 revokedKeyboard: system onlyBrowser extensions: 5 removed# 08 · apps & keyboardspolicy apps {allow = approved_listmic_camera = reviewkeyboards = system_only}revoke → 14 permissionsremove → 5 extensionsapply → phone, laptop ✓ -
How it happens. A laptop left in a hotel room or an empty office can be copied or fitted with a keylogger in minutes if the disk is not encrypted.
What we set up. Full-disk encryption, a firmware password, lock on lid close, a privacy filter for travel.
Disk encryption: onFirmware password: setLock on lid close: on# 09 · unencrypted laptoppolicy laptop.disk {encryption = full_diskfirmware_pass = setlock_on_lid = trueprivacy_filter = travel}apply → laptop ✓
This is how the devices look once ISMO has set them up — for the whole team, not only for the owner.
Check my team's devicesSome leaks need no insider at all
A transmitter in the meeting room, a tracker on the company car, a gift that listens. Find them yourself — then think of the rooms nobody has checked.
Five pictures: meeting room, CEO office, open space, car and devices. Every object that can be checked lights up when the pointer is over it. The detector beside the pointer shows how close a hidden device is: the more bars, the closer. Activating an object inspects it and shows what was hidden there, or that it is clean. On a touch screen, pick up the scanner under the picture and move it over the room: its bars rise as it nears a hidden device, and a find opens a card with the explanation. A tap on an object also inspects it. With a keyboard, Tab moves between the objects and shows the detector reading for each. Found devices stay marked. When a picture is complete, a button leads to the next one.






Pick up the scannerDrag it over the room: the closer to a hidden device, the stronger the signal.
Everything found
On a real sweep we find these with a spectrum analyser, a non-linear junction detector, thermal imaging and a hands-on inspection — and check the network the same day.
Order a premises sweepWhen it has already happened, the first hour decides what you can prove
We record the incident, preserve the evidence, run interviews inside a lawful internal procedure and prepare the material for wherever it has to go next.
Select a stage.
Nature, scale and consequences written down before memories and logs change.
Logs, devices, messages and documents secured in a way that still counts later.
Conversations run inside a lawful internal procedure, with a record of each one.
A written account for the owner: what happened, who was involved, what it cost, what to change.
Criminal, civil, administrative or commercial — in the jurisdiction where it has to be heard.
Three steps. The third one never ends
Internal security is not a project with a delivery date. It starts with a look, becomes a set of rules, and then simply runs — the way finance or legal runs.
Risk X-Ray
A fixed-scope first look. Who holds what, where money and data can leave, which roles carry the most exposure. You get a written assessment and a priority list — and no obligation to continue.
Setup
Policies, access map, device and messenger protocols, onboarding and offboarding. Your rules, written down, in force, and understood by the people they apply to.
Standing office
Screening before every hire, monitoring while people work, risk reporting to the owner, and the investigation on the day it is needed. One contract, one party answering for all of it.
An internal department cannot investigate itself
Independent
We report to the owner, not to the department under review. No one grades their own homework.
From screening to evidence
Screening, monitoring and investigations in one contract. Every assessment and every incident is recorded so the material still counts later.
Lighter, not heavier
HR, IT and Legal stop carrying security work they were never built for.
NDA first
Nothing is discussed in detail before a non-disclosure agreement is signed. Only the officers assigned to you see your material, and the list is yours to review.
No names
We never publish or mention clients — not in case studies, not at conferences. That is the whole point of the service.
Material under control
Stored encrypted, every access logged, deleted at the end of the contract with written confirmation. Checks run only within the law and with the consents it requires.
Request a Risk X-Ray or ask a question — everything under NDA
Request received
Thank you. A named officer will reply within one business day.
Your reference: —